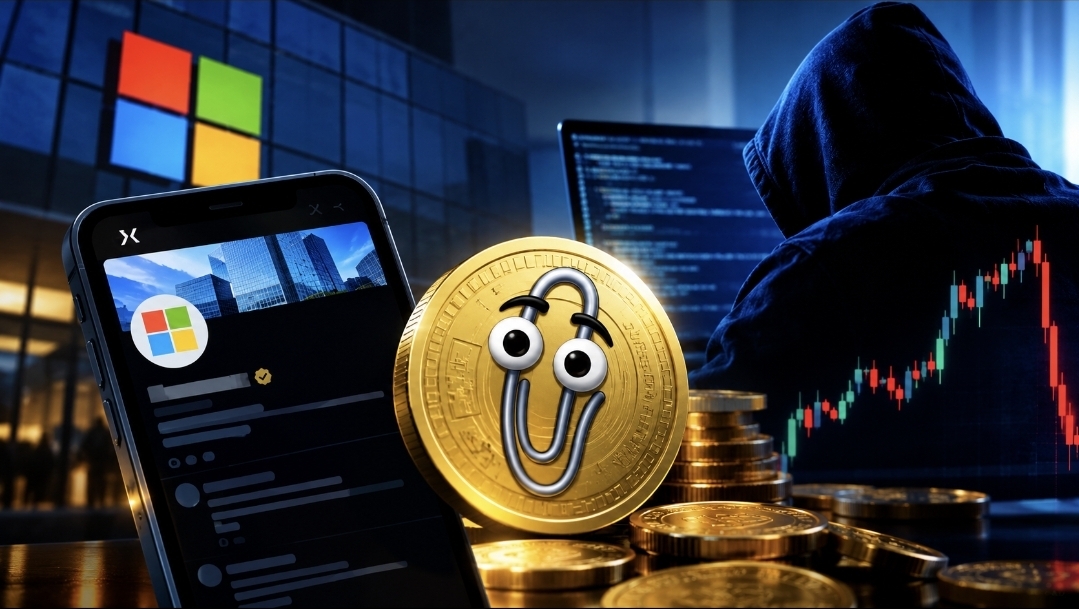
Microsoft’s official X account was hacked and used to promote an unauthorized Clippy themed cryptocurrency, exposing more than 13 million followers to a meme coin campaign that appeared designed to exploit the credibility of the technology giant’s verified social media presence. Microsoft later confirmed that attackers gained unauthorized access to the account and published posts that did not come from the company.
The incident targeted the main Microsoft account on X, rather than a smaller regional or product specific profile. During the compromise, the account followed an account impersonating Microsoft’s famous Clippy assistant, reposted its content and changed its profile picture to an image of Clippy, the paperclip character associated with older versions of Microsoft Office.
Hackers Used Microsoft’s X Account to Push $Clippy
The compromised Microsoft X account amplified posts connected to an unofficial cryptocurrency called $Clippy. The operation centered on nostalgia for Clippy while attempting to make the token appear connected to Microsoft through the company’s own social media account.
According to reports, the Microsoft account followed clippymsftcto, an account that presented itself as being associated with Clippy, before reposting one of its messages. X later suspended that account. Another account, ClippyMSFT, continued promoting the token and claimed that its liquidity pool was paired with $MSFT, Microsoft’s stock ticker.
Microsoft explicitly rejected any connection between the cryptocurrency and the company. A statement posted during the incident and later deleted said Microsoft had not authorized, sponsored or endorsed a cryptocurrency connected to Clippy, Microsoft or $MSFT. Reports also said the statement rejected any suggestion that holding the token represented ownership of Microsoft shares.
The reported claims surrounding the token remained unverified, including suggestions about liquidity linked to Microsoft stock. Microsoft’s confirmation instead established that its account had been accessed without authorization and that the cryptocurrency promotion did not originate from the company.
Microsoft Secures Account After Unauthorized Posts
The unauthorized activity lasted roughly 30 minutes before the promotional posts disappeared, according to reporting. During that period, the attackers had access to a highly visible corporate account with more than 13 million followers, giving the cryptocurrency campaign exposure that an ordinary newly created meme coin account would struggle to obtain.
Microsoft later confirmed that it had secured the account and removed the unauthorized posts. A company spokesperson said Microsoft had confirmed unauthorized access to its X account and was continuing to investigate the circumstances surrounding the incident.
The incident demonstrates how compromised social media accounts can become tools for cryptocurrency scams. Attackers can exploit the reputation, follower base and verification associated with a major company to make unauthorized cryptocurrency promotions appear legitimate to users who encounter them during a fast moving campaign.
The incident also highlights the risks surrounding meme coins that borrow recognizable corporate brands, characters or stock tickers. In this case, the attackers combined Clippy’s familiarity with Microsoft’s official social media presence to promote a cryptocurrency that the company said it had never authorized.
Microsoft Has Faced Previous X Account Crypto Attacks
The Clippy incident is not the first time attackers have targeted a Microsoft owned X account for cryptocurrency related activity. In June 2024, scammers compromised Microsoft India’s X account and used it to impersonate meme stock trader Keith Gill, also known as Roaring Kitty, in a cryptocurrency promotion.
The latest breach adds to a wider pattern of hackers targeting prominent social media accounts to promote cryptocurrency tokens. Compromised accounts belonging to well known companies and public figures can provide attackers with immediate visibility and a false appearance of endorsement.
For users, the Microsoft incident reinforces the importance of verifying cryptocurrency announcements through multiple independent sources, even when a promotion appears on an official corporate account. A verified or widely followed social media profile can still become compromised, and an unauthorized post does not represent the views or endorsement of the account owner.
Microsoft has removed the unauthorized content and said its investigation remains ongoing. The company has not publicly disclosed how attackers obtained access to the X account or provided further technical details about the compromise.