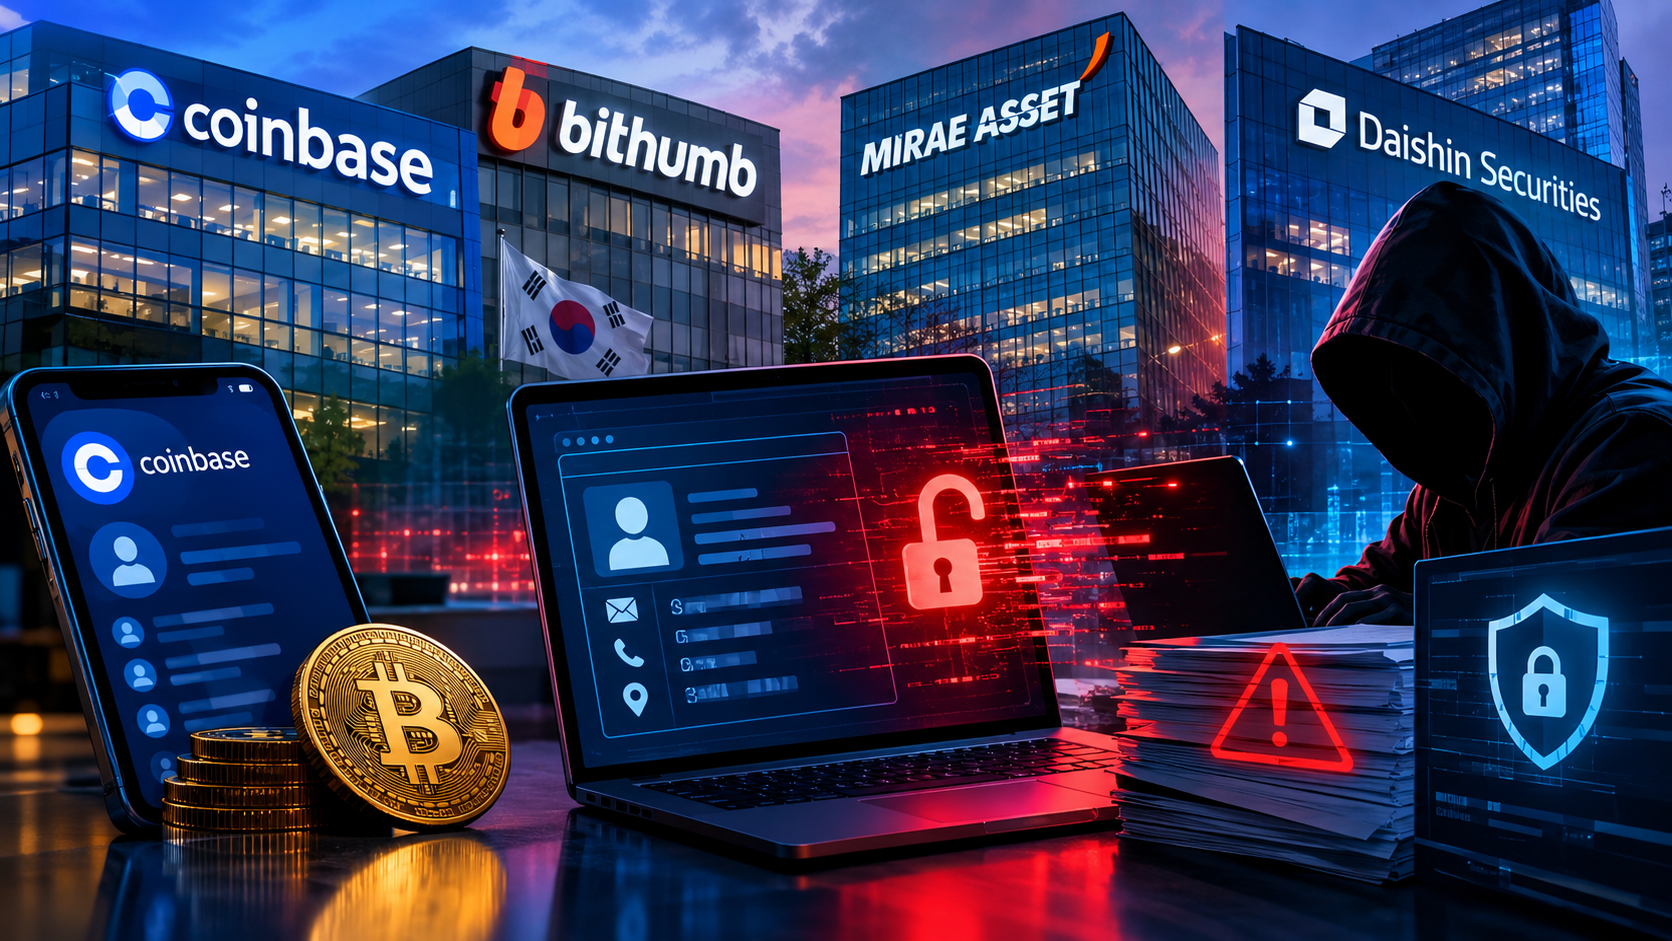
Four financial and cryptocurrency companies have reported separate data security incidents, raising fresh concerns about customer privacy and cybersecurity across the digital asset and traditional finance industries. The incidents involve Coinbase’s analytics provider Amplitude, South Korean cryptocurrency exchange Bithumb, Mirae Asset Global Investments, and Daishin Securities.
The disclosures, reported on October 28, 2026, highlight the growing risks associated with third-party service providers, internal business systems, and financial platforms that handle sensitive customer information. While the incidents differ in scope and severity, they underline how exposed personal information can create security risks even when attackers do not directly access customer funds.
Among the four cases, Daishin Securities disclosed that personal and credit information belonging to 38,490 customers had been exposed. Coinbase, meanwhile, attributed the exposure of some customer contact information to a security incident involving Amplitude, an external analytics provider. Bithumb and Mirae Asset also reported separate security incidents in South Korea.
Coinbase and Amplitude Report Customer Data Exposure
Coinbase confirmed that a security incident involving Amplitude exposed contact information belonging to a small subset of its customers. The cryptocurrency exchange clarified that the incident originated with its third party analytics provider rather than its own internal systems.
According to Coinbase, investigators found no evidence of unauthorized access to its systems, and customer funds remained unaffected. The company has not publicly disclosed the exact number of affected customers or provided a complete breakdown of the exposed information. Coinbase said it would notify affected customers through email as required.
The incident highlights the cybersecurity risks that cryptocurrency exchanges face when they rely on external vendors for analytics and other technical services. Even when an exchange maintains its own security controls, a vulnerability involving a third-party provider can expose customer information and create opportunities for phishing attacks, impersonation, and social engineering.
For cryptocurrency users, exposed contact information can become a starting point for scams that imitate legitimate exchange communications. Criminals may use leaked email addresses or phone numbers to send fraudulent security alerts, impersonate customer support agents, or persuade victims to reveal account credentials and authentication codes. Coinbase’s statement that customer funds remain safe is reassuring, but users should still treat unexpected messages claiming to come from the exchange with caution.
Bithumb, Mirae Asset and Daishin Securities Face Security Incidents
South Korean cryptocurrency exchange Bithumb reported unauthorized access to its internal mobile groupware system, which employees use for workplace communications and other business activities. The company discovered the incident on October 27 and reported it to the relevant South Korean authorities.
Bithumb is investigating the extent of the information exposure, including whether customer details were among the compromised records. The exchange has indicated that its internal work system operates separately from its cryptocurrency trading infrastructure. However, the investigation must establish the full scope of the incident before the company can provide a definitive account of the information affected.
Mirae Asset Global Investments also reported unauthorized access to certain internal business systems. The company said the incident involved information used for internal operations but maintained that general investors’ personal and credit information had not been compromised. It also reported no financial losses or service interruptions associated with the incident.
Daishin Securities disclosed the most clearly quantified customer data exposure among the four cases. The South Korean brokerage confirmed that personal and credit information belonging to 38,490 customers had been exposed following suspicious activity involving a server connected to its remote brokerage account opening service.
The exposed information included names, email addresses, residential addresses, communication IDs, bank names, deposit and withdrawal account numbers, securities account numbers, and mobile phone numbers. Daishin said certain financial account details and mobile phone numbers were encrypted. The company has reported no evidence of secondary damage so far and said it would notify affected customers and address qualifying losses in accordance with applicable legal requirements.
Together, the incidents at Bithumb, Mirae Asset, and Daishin Securities demonstrate that cybersecurity risks extend beyond cryptocurrency exchanges. Traditional financial institutions also face threats involving customer databases, externally connected services, and internal business infrastructure. South Korean authorities are examining the reported incidents as concerns about financial sector data protection continue to grow.
Data Leaks Raise Phishing and Cybersecurity Concerns
The four incidents highlight the importance of protecting personal information across cryptocurrency platforms, investment firms, and third party technology providers. Although a data leak does not automatically mean that attackers can withdraw funds, exposed customer details can help criminals develop more convincing phishing campaigns and account takeover attempts.
Cryptocurrency users should strengthen their account security by using unique passwords for every financial platform and enabling two factor authentication through an authenticator app or hardware security key. Where supported, passkeys can offer another strong authentication option. Users should also review active sessions, remove unfamiliar devices, and revoke API keys they no longer need.
Customers should remain alert to unsolicited emails, phone calls, and messages claiming to offer account recovery, security assistance, or compensation following a breach. Legitimate support teams should never need a user’s password, wallet seed phrase, or private key. Users should access their accounts through official applications or verified websites instead of clicking links in unexpected messages.
The incidents also reinforce the need for financial institutions to strengthen third party vendor assessments, restrict access to sensitive systems, monitor unusual activity, and respond quickly when they detect unauthorized access. Companies that handle customer information must consider how attackers could exploit exposed data even when their core trading or banking infrastructure remains secure.
As investigations continue, the full impact of the four reported incidents may become clearer. For now, the Coinbase Amplitude exposure, Bithumb incident, Mirae Asset security issue, and Daishin Securities data leak serve as a reminder that cybersecurity requires continuous attention across both the cryptocurrency and traditional finance sectors.