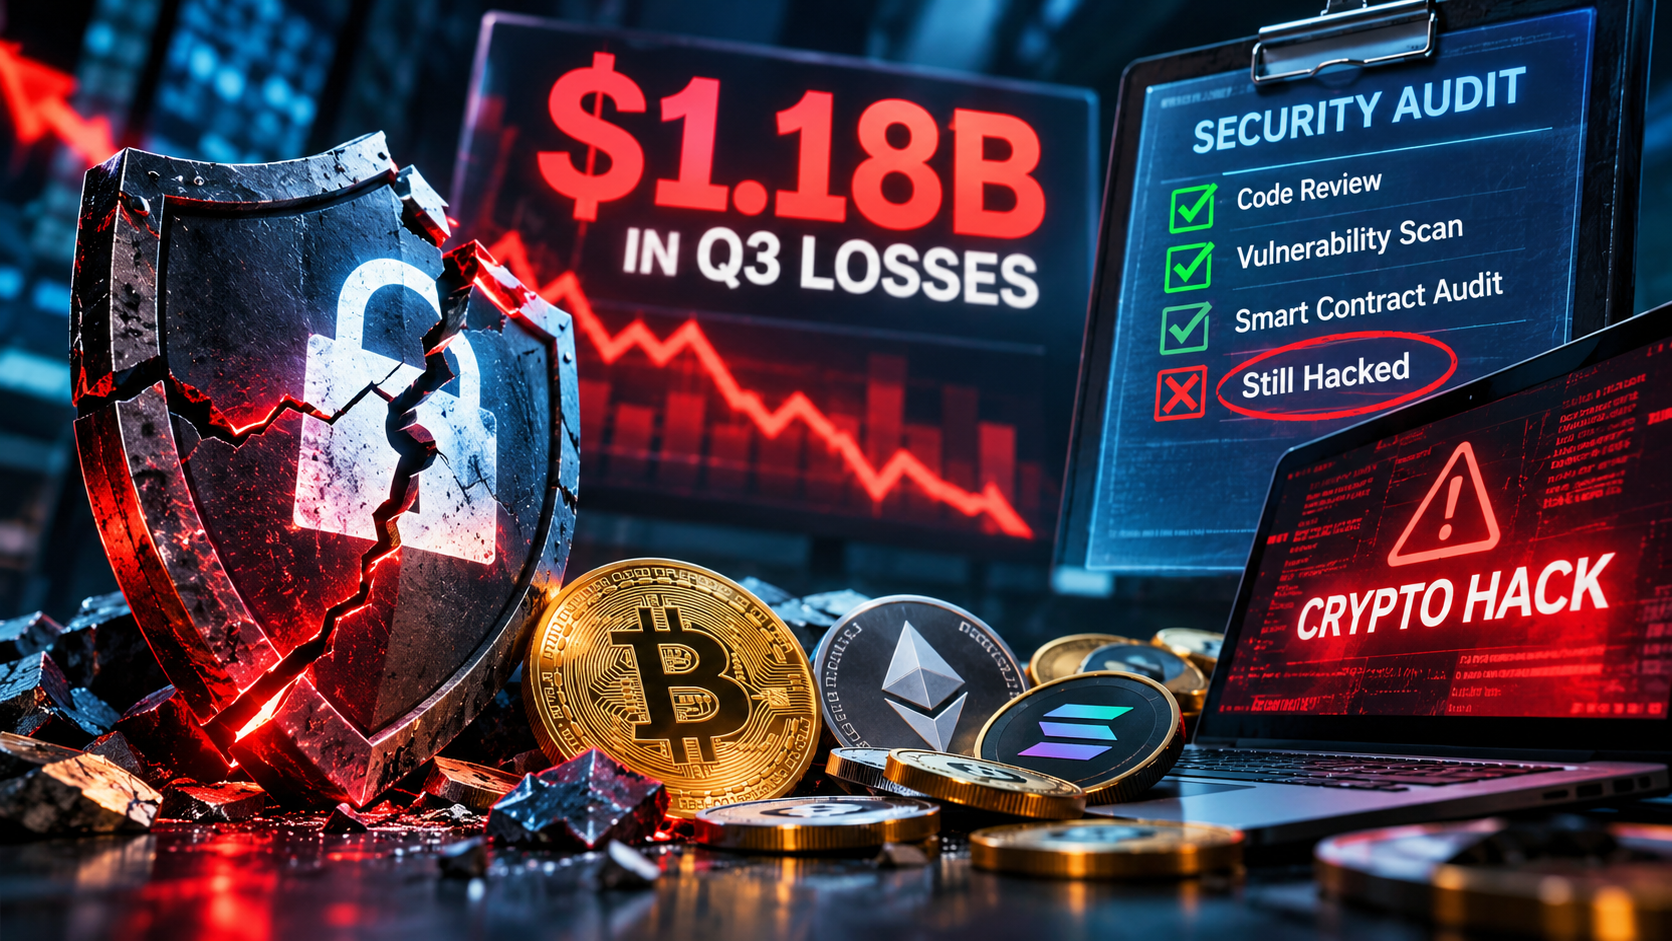
Crypto security audits are under fresh scrutiny. Hacken counted $1.18 billion in losses across 107 digital-asset incidents in Q3 2026. That was 55% more than in Q2. The figures do not mean every audit failed. They show that a code review cannot cover every risk around a crypto project.
CoinDesk reported on October 18 that 77% of Q3 losses involved compromised suppliers, delayed fixes, or systems outside the latest reviews. An audit helps, but it cannot replace strong day-to-day security.
What Crypto Security Audits Tell Us About Q3 Losses
Hacken’s Q3 2026 Security and Compliance Report tracks 107 incidents from July to September. It puts losses at $1.18 billion. Smart-contract exploits made up 48% of the total, up from 12% in Q2.
These figures come from Hacken’s own tracking. They are not a full count of every crypto loss. Still, they show how fast attacks can hurt projects and users.
Why Crypto Security Audits Cannot Guarantee Safety
An audit checks a set code version and a defined scope. It may find flaws in that code. It does not protect staff accounts, cloud systems, signing keys, vendors, or later software changes by itself. Teams can add new risks after the review.
Before trusting an audit, check which code version it covered. Ask whether the team fixed the issues it found. Look for a follow-up review. Check that the project shares updates when its code or security setup changes.
Security Controls That Should Support an Audit
Code review alone is not enough. Crypto security audits work best with other safeguards. Projects can split signing power and require more than one approval for large transfers. They can limit withdrawal rights and watch for unusual activity. They should also control vendor access, test updates, and practise incident response.
No single step removes all risk. But these controls can limit damage when a flaw or account is exposed. Projects should explain how they protect funds after an audit, not just display a badge.
How Users Should Read These Findings
Hacken’s report does not show that audits are useless. Audits remain one layer of safety. The key question is whether a project keeps its code, keys, vendors, access rights, and monitoring safe over time.
Before depositing a large amount, review the audit scope, past incidents, and any open findings. Be careful if a team gives few details about its controls. For a related example of an attack that went beyond ordinary software checks, read our coverage of the Lazarus-linked crypto investigation.
Sources: Hacken, Q3 2026 Security and Compliance Report; CoinDesk, October 18, 2026.